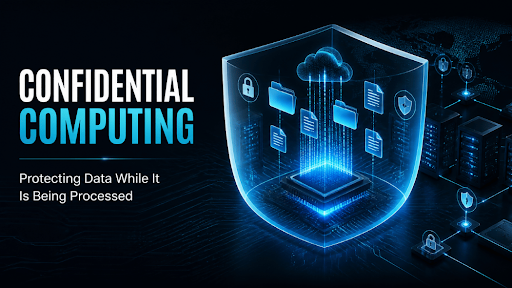
Learn how confidential computing protects sensitive data during processing, strengthens cloud security, and helps businesses maintain data privacy.
What Is Confidential Computing?
Businesses store large amounts of sensitive information across cloud platforms, databases, and internal systems. Protecting this information has become a major responsibility. Traditional security methods protect data while it is stored or transferred. However, data also needs protection when applications actively use it.
This is where confidential computing becomes important.
Confidential computing is a security technology that protects data while it is being processed. It uses hardware-based Trusted Execution Environments (TEEs) to isolate sensitive workloads from other software, including privileged system components. This helps prevent unauthorized access to information during computation.
For example, consider a healthcare company processing patient records through a cloud application. Encryption can protect those records while they travel across networks or remain in storage. But applications must decrypt and process the information to perform calculations. Confidential computing adds another layer of protection during this stage.
The technology is gaining attention among organizations that handle financial records, medical information, customer databases, and confidential business documents. It also supports businesses that want to use cloud infrastructure without exposing sensitive workloads unnecessarily.
How Does Confidential Computing Work?
Confidential computing uses specialized hardware and security mechanisms to create an isolated environment for processing sensitive information. This environment is commonly known as a Trusted Execution Environment.
A TEE separates protected workloads from the wider operating system and other applications. Even if another part of the system becomes compromised, the isolation helps prevent unauthorized access to protected memory.
Here is how the process generally works.
1. Creating a Trusted Execution Environment
The processor creates a protected area of memory where sensitive applications can run. Only authorized code can access the resources inside this environment.
The operating system and other applications cannot freely inspect the protected workload. This separation reduces exposure to certain types of attacks.
2. Loading Sensitive Data
Once the protected environment is ready, the application loads the required information into it.
The data remains protected through hardware-supported memory encryption and access controls. This makes it harder for unauthorized software to read information directly from system memory.
3. Processing Information Securely
The application performs its required operations inside the protected environment.
For example, a financial organization can process customer transaction records without exposing the entire dataset to other software running on the same infrastructure.
4. Verifying the Environment
Many confidential computing systems support a process called remote attestation.
Attestation allows an external system to verify that a workload is running inside an expected trusted environment. It can also provide evidence about the hardware and software configuration.
This verification helps organizations decide whether sensitive information should be released to a particular workload.
5. Returning the Results
After processing is complete, the application returns the required output to the authorized system.
The information can then move through normal business workflows, subject to the organization’s security policies.
Why Is Confidential Computing Important for Businesses?
Cloud computing has changed how organizations store and process information. Companies can now access powerful infrastructure without maintaining every server themselves.
However, sharing infrastructure also creates security considerations. Businesses need confidence that their sensitive workloads remain protected.
Confidential computing addresses part of this challenge.
Protecting Sensitive Business Information
Organizations process confidential information every day. This includes customer details, financial records, employee information, and internal business documents.
A traditional encryption strategy protects data at rest and in transit. Confidential computing adds protection while applications use that data.
This is particularly useful for businesses working with sensitive datasets or external cloud providers.
Improving Cloud Security
Cloud environments often involve multiple applications, services, and administrative layers. A security weakness in one component can increase the risk of unauthorized access.
Confidential computing introduces hardware-backed isolation for supported workloads. It reduces the level of trust businesses must place in certain infrastructure components.
However, it does not replace cloud security controls, identity management, or regular vulnerability testing.
Supporting Data Privacy Requirements
Companies operating in regulated industries must follow strict rules for handling personal and financial information.
Confidential computing can support privacy-focused processing by reducing unnecessary exposure of sensitive data.
Organizations must still assess applicable privacy laws, contractual requirements, data residency rules, and compliance obligations. Using confidential computing alone does not guarantee regulatory compliance.
Enabling Secure Collaboration
Sometimes, multiple organizations need to analyze shared information without exposing their complete datasets to one another.
For example, financial institutions may want to identify suspicious transaction patterns across different datasets.
Confidential computing can help create protected processing environments for these workloads. Each organization can maintain greater control over its sensitive information while approved computations take place.
Real-World Applications of Confidential Computing
Confidential computing is not limited to large technology companies. Its applications extend across several industries.
1. Healthcare and Medical Research
Healthcare organizations handle patient records, diagnostic reports, treatment histories, and research information.
Researchers often need large datasets to study diseases and evaluate medical treatments. However, sharing identifiable patient information creates privacy concerns.
Confidential computing can support protected analysis of sensitive medical datasets. Authorized applications can process information within isolated environments.
Hospitals, research institutions, and healthcare technology providers can explore this approach for privacy-sensitive workloads.
2. Banking and Financial Services
Banks process transaction records, credit information, customer identities, and payment details.
Financial institutions can use confidential computing to protect selected workloads involving fraud detection, risk assessment, and financial analysis.
For example, a bank may process sensitive customer information through a protected environment while running a risk assessment model.
This helps reduce exposure during computation, although application security and access controls remain essential.
3. Cloud Computing and SaaS Platforms
Cloud service providers offer infrastructure to businesses across different industries.
Some organizations hesitate to move sensitive workloads to shared cloud environments because they have concerns about infrastructure access and data exposure.
Confidential computing can help address these concerns through hardware-backed workload isolation.
Businesses can also explore confidential virtual machines and confidential containers for applications that require additional processing protection.
4. Artificial Intelligence and Machine Learning
AI development often involves large datasets containing proprietary or personal information.
Companies may want to run machine learning workloads without exposing sensitive training data or model information to unnecessary infrastructure components.
Confidential computing can provide protected environments for certain AI workloads. It may also support collaborative machine learning projects where different organizations need to process sensitive datasets.
However, hardware support, performance requirements, model architecture, and the software environment must be evaluated before deployment.
5. Government and Public Sector
Government departments handle sensitive citizen records, administrative information, and confidential operational data.
Confidential computing can help protect selected workloads when public institutions use cloud infrastructure or collaborate with external technology providers.
It offers another security layer for processing information that requires strict access controls.
Confidential Computing vs Traditional Data Encryption
Traditional encryption and confidential computing serve related but different purposes.
Encryption protects information when it is stored or transferred. Confidential computing focuses on protecting supported workloads while information is being processed.
Consider these three stages:
Data at Rest: Information is stored in databases, storage systems, or backup environments. Encryption protects it from unauthorized access.
Data in Transit: Information moves between applications, servers, or networks. Transport encryption protects it during communication.
Data in Use: Applications access information to perform calculations, analysis, or other operations. Confidential computing uses hardware-backed isolation to protect supported processing environments.
These approaches work best together. Businesses should not treat confidential computing as a replacement for existing encryption methods.
What Are the Main Challenges of Confidential Computing?
Despite its security benefits, confidential computing also has limitations. Businesses should understand these challenges before adopting the technology.
Hardware Compatibility
Confidential computing depends on supported processor features and platform capabilities.
Not every server or cloud environment supports the same technologies. Organizations must check hardware compatibility before moving workloads.
Performance Considerations
Creating protected environments and applying additional security controls can introduce performance overhead.
The impact depends on the hardware, workload, memory requirements, and implementation. Businesses should conduct performance testing before deploying critical applications.
Application Changes
Some applications require modifications to work inside confidential environments.
Legacy systems may need additional development, configuration, or testing. This can increase implementation time and costs.
Security Does Not Cover Everything
Confidential computing protects specific parts of the processing environment. It does not automatically prevent every cybersecurity threat.
For example, malicious application code, stolen credentials, insecure APIs, and poorly configured access permissions can still create security risks.
Businesses should combine confidential computing with strong identity management, encryption, monitoring, and regular security assessments.
How Can Businesses Start Using Confidential Computing?
Organizations do not need to move every application into a confidential environment immediately. A gradual approach makes adoption easier to manage.
Here are some practical steps.
- Identify sensitive workloads: Start with applications that process financial records, customer information, healthcare data, or intellectual property.
- Review infrastructure compatibility: Check whether existing processors and cloud platforms support confidential computing features.
- Evaluate cloud providers: Compare available confidential virtual machines, hardware security features, supported regions, and service limitations.
- Test a small application: Select one workload and evaluate its performance, compatibility, and security requirements.
- Implement access controls: Use strong authentication, restricted permissions, encryption, and secure key management.
- Monitor performance and security: Review application behavior, system logs, attestation results, and operational costs.
Businesses should also review their broader AI implementation mistakes before introducing new technologies. Poor planning, weak data governance, and insufficient testing can affect even well-designed security projects.
The Future of Confidential Computing
As businesses move more workloads to cloud infrastructure, protecting sensitive information during processing will remain important.
Confidential computing is likely to play a larger role in privacy-focused cloud services, financial data processing, healthcare research, and enterprise applications.
Its connection with AI is also worth watching. Organizations want to process proprietary information through advanced computing systems while maintaining control over sensitive datasets.
Developments in processor security, remote attestation, confidential containers, and cloud infrastructure will influence how quickly businesses adopt the technology.
Companies already investing in cloud-based business automation may also find confidential computing useful when their automated workflows handle sensitive information.
The technology will not eliminate cybersecurity risks. However, it can reduce exposure at a stage that traditional encryption does not fully address.
Frequently Asked Questions
1. What is confidential computing in simple terms?
Confidential computing protects sensitive information while a computer application is actively processing it. It uses hardware-based secure environments to prevent unauthorized access to supported workloads.
2. How is confidential computing different from encryption?
Encryption protects data while it is stored or transferred. Confidential computing adds protection while applications process information inside a trusted execution environment.
3. What is a Trusted Execution Environment?
A Trusted Execution Environment is an isolated area within supported hardware. It allows authorized applications to process sensitive information with additional protection from other software.
4. Is confidential computing completely secure?
No technology provides complete protection against every threat. Confidential computing reduces certain risks, but businesses still need secure applications, access controls, encryption, monitoring, and regular testing.
5. Which industries can benefit from confidential computing?
Healthcare, banking, insurance, government, cloud computing, and technology companies can benefit from confidential computing when they process sensitive information.
6. Does confidential computing work with cloud platforms?
Yes. Several cloud platforms offer confidential computing capabilities through supported virtual machines and other services. Availability depends on the provider, hardware, region, and workload.
Final Thoughts
Confidential computing addresses an important gap in traditional data protection. It helps protect sensitive information while applications actively process it.
For businesses handling financial records, healthcare information, customer databases, or proprietary data, this approach offers another layer of security.
However, successful implementation requires more than selecting compatible hardware. Organizations must evaluate application requirements, access controls, infrastructure, and performance.
When combined with encryption and established cybersecurity practices, confidential computing can help businesses build more secure data processing environments.

+ There are no comments
Add yours